SOC2

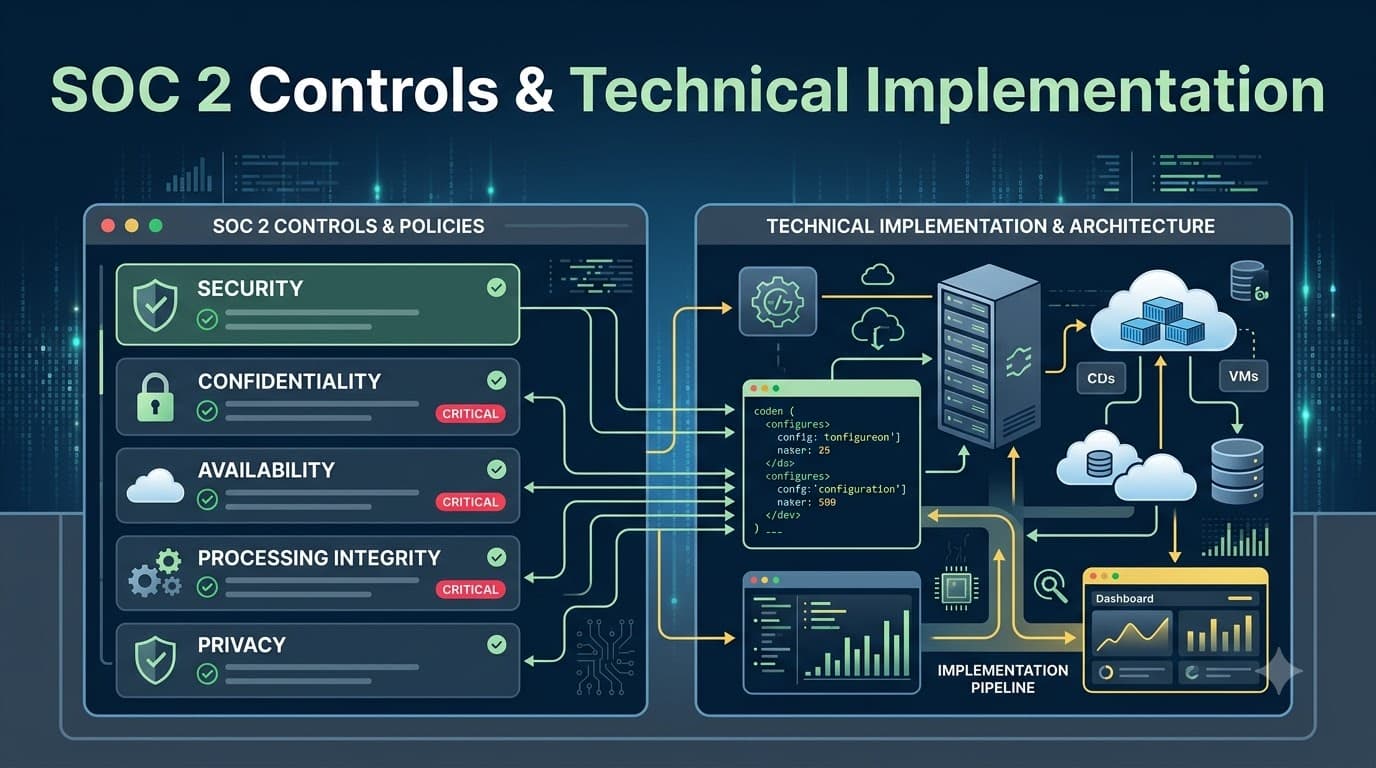
SOC 2 Controls & Technical Implementation

How to implement and evidence the technical controls a SOC 2 tests. Back to SOC 2: The Complete Guide.

SOC 2 Controls & Technical Implementation
Loading advertisement...
12

How to implement and evidence the technical controls a SOC 2 tests. ← Back to SOC 2: The Complete Guide

Guide

Focus

Access Controls: User Management & Privileges

CC6 — provisioning, reviews, privileged access

Logical Security: Access & Authorization

CC6 — authN/authZ, MFA, RBAC

Network Security Controls

CC6 — perimeter & internal protection

Data Backup & Recovery

Availability — backups, RTO/RPO

Change Management

CC8 — system & application updates

Incident Response: Event Management

CC7 — detect, respond, recover

Vulnerability Management

CC7 — scanning & remediation

Encryption Controls

CC6 — at rest & in transit

Security Monitoring: SIEM & Logs

CC7 — logging & monitoring

Physical Security

CC6 — data center & office

Environmental Controls

Availability — infrastructure protection

System Configuration & Hardening

CC7 — baselines

Patch Management

CC7 — update & testing

Malware Protection & Endpoint Security

CC6.8

Data Classification

CC6/Confidentiality

Resources: Control Matrix / RACI · Policy Pack · Gap Analysis Tool

12

About the author

Cybersecurity Expert

Satish Kumar writes about cybersecurity, offensive security, and practical defense strategies on PentesterWorld.

Related Articles

Comments (0)

No comments yet. Be the first to share your thoughts!