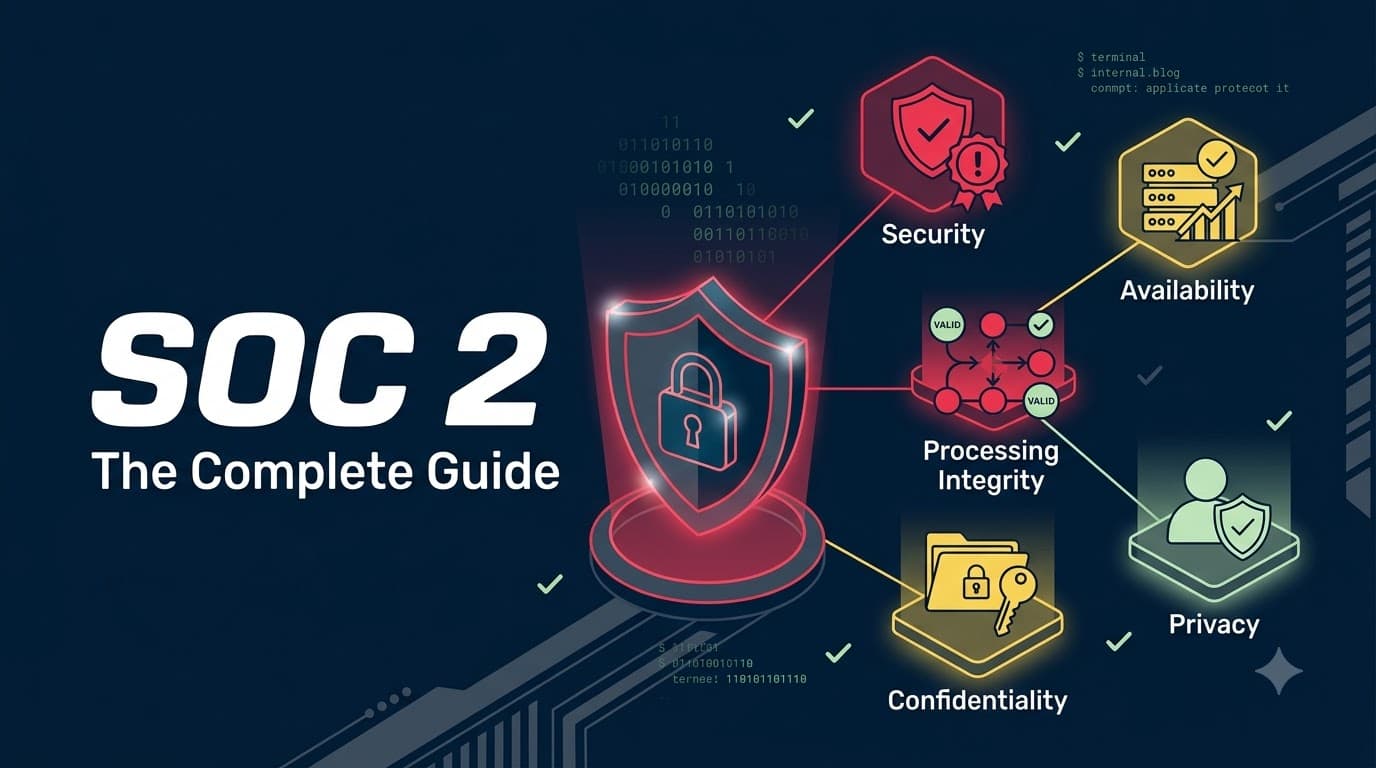
Everything you need to understand, prepare for, and pass a SOC 2 examination. SOC 2 is the AICPA attestation report — performed by a licensed CPA firm — that proves your controls meet the Trust Services Criteria, and it's the default trust signal buyers ask software and service companies for. This is the home of PentesterWorld's SOC 2 library: 90 in-depth guides plus templates, checklists, calculators, and quizzes.
New to SOC 2? Start with the SOC 2 Complete Guide to the Trust Services Criteria, then take the free Are You SOC 2 Ready? quiz.
Explore by topic
Foundations & Overview — what SOC 2 is, Type I vs II, the SOC family, reports, scope, and readiness.
Trust Services Criteria — Security (CC1–CC9) plus Availability, Processing Integrity, Confidentiality, and Privacy.
Controls & Technical Implementation — access, network, encryption, monitoring, change, incident, backup, and more.
Industry & Technology Guides — SaaS, cloud, FinTech, healthcare, MSPs, and 10 more sectors.
Audit Process & Management — auditor selection, evidence, testing, exceptions, cost, and the final report.
Practical Implementation — first-time roadmap, timeline, policies, vendor management, and sales enablement.
Start here — essential guides
If you want to… | Read this |
|---|---|
Understand SOC 2 from scratch | |
Choose Type I or Type II | |
See the business case | |
Get audit-ready | |
Run the whole project | |
Budget for it | |
Decide SOC 2 vs ISO 27001 |
Free tools & downloads
Gap Analysis Tool · Cost Calculator · Readiness Quiz · Readiness Checklist · TSC Mapping Template · Control Matrix / RACI · Policy Pack · Report Reader's Guide (eBook) · SOC 2 Glossary